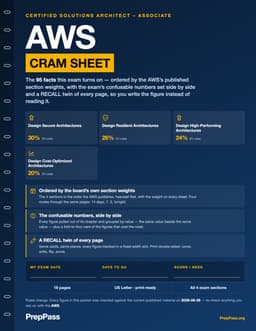
Design Secure Architectures
An application running on EC2 instances needs to read objects from an S3 bucket. What is the most secure way to grant this access?
- AStore long-lived credentials in a file on the instance
- BMake the S3 bucket public and filter by source IP
- CAttach an IAM role to the EC2 instances with a policy granting least-privilege S3 read accessCorrect
- DEmbed an IAM user's access keys in the application code
Why: IAM roles provide temporary, automatically rotated credentials to EC2 instances via the instance metadata service, eliminating the need to store long-lived keys. Scoping the role's policy to only the required bucket and actions follows the principle of least privilege. Hard-coded access keys and public buckets create serious security risks and violate the Security pillar of the Well-Architected Framework.